NIS2 and GDPR compliance
Documents, measures and evidence to comply with NIS2 and GDPR, even if you supply a company that is in scope.
The service in detail
The NIS2 directive, transposed in Italy by Legislative Decree 138/2024, requires many companies to have documented security measures, to report incidents within set deadlines and to check their suppliers. Even companies not directly in scope are asked for it by their clients.
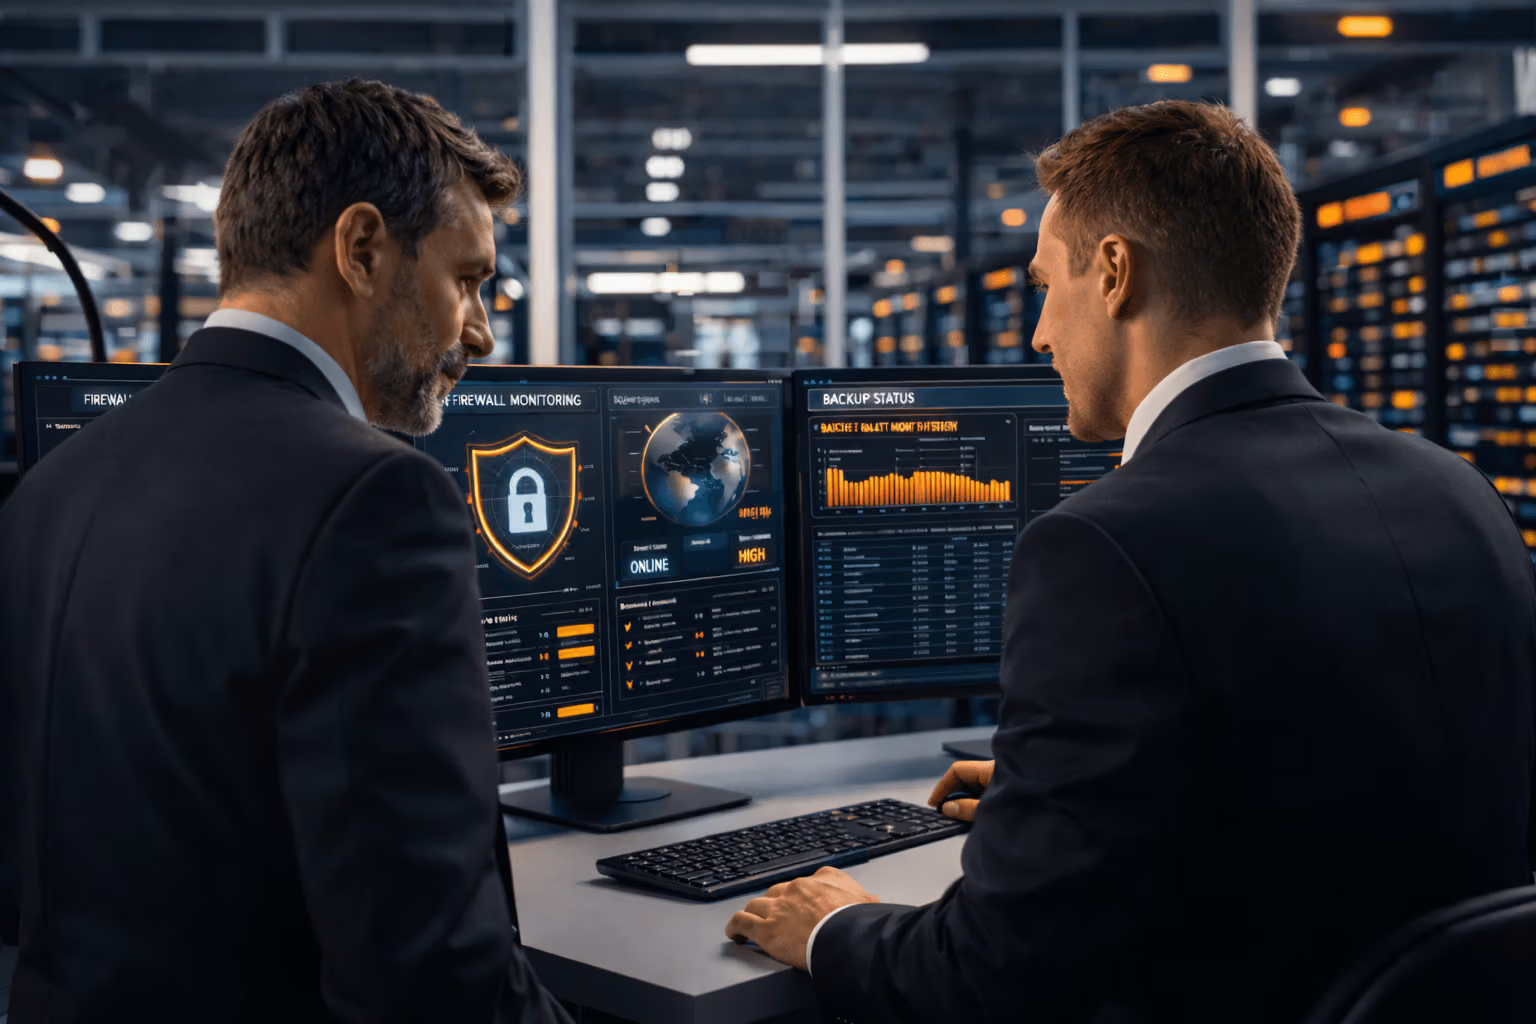
We prepare a single, consistent set of NIS2 and GDPR documents and keep it alive with the evidence coming from our managed services: verified backups, firewalls, device protection, access. So what is written matches what actually happens.
The Cybernix website explains the directive for the Italian sites of international companies.
How we work
Always on
Continuous monitoring and support for your infrastructure.
Dedicated team
Certified technicians who know your company.
Certifications
Certified partners of the leading technology vendors.
Other Cybersecurity services
Is your company really protected?
Let’s start with a free assessment: we tell you what works and what needs improving, before an attacker finds out.